

Managed IT Services in Branford, CT
IT for Branford’s shoreline community, Yale-adjacent businesses, healthcare practices, and established professional economy.
Schedule Your IT Assessment
Branford sits one town east of New Haven and has quietly become a destination for businesses that want Yale’s research ecosystem within reach without paying New Haven commercial rents. Small life sciences companies, medical device firms, and technology businesses in Branford’s Route 1 and commercial office corridors carry the compliance requirements of organizations in the Yale orbit: FDA data integrity expectations, research partnership data governance, and the vendor security assessments that enterprise health system customers send. New Haven’s page serves the Science Park core. Branford is where that ecosystem’s edge meets the Connecticut shoreline.
Yale New Haven Health-affiliated practices serve Branford’s 28,000 residents and connect the town to one of Connecticut’s largest health networks. The Long Island Sound coastline through Stony Creek, Indian Neck, and Pine Orchard adds a seasonal commercial dimension: independent restaurants, marine services, boat yards, and waterfront businesses whose revenue concentrates in summer. Professional services firms serving an established residential community round out a market that is more self-contained than New Haven’s innovation economy and more sophisticated than its size suggests. SII builds programs for each of these communities around what they actually carry.

What IT Failure Costs Branford Organizations
Branford’s life sciences businesses, healthcare practices, shoreline commercial operations, and professional services firms carry real compliance obligations and operational dependencies where reactive IT creates vulnerabilities that grow more consequential as customer expectations and regulatory frameworks tighten.
- Research data governance failures at Branford's Yale-adjacent life sciences companies when data use agreements or FDA-regulated data environments lack the access controls and audit trails that research partnerships and regulatory submissions require, creating findings that affect both academic relationships and commercial development timelines
- HIPAA incidents at Yale New Haven Health-affiliated practices serving Branford's residential shoreline community, where a breach affecting long-tenured patients triggers federal notification obligations and damages the neighborhood trust that community practices build over years of consistent care
- Client data exposure at Branford's professional services firms when client records, financial documents, and confidential matter files are inadequately protected, triggering Connecticut professional conduct obligations and the personal trust damage that follows a confidentiality failure in a close-knit shoreline community
- Seasonal IT failures at Branford's coastal restaurants, marinas, and shoreline commercial operations during summer peak weeks when POS systems, reservation platforms, or connectivity fails at the highest-revenue moments of the year and off-season months cannot compensate for the lost revenue
- Ransomware attacks on Branford's commercial businesses and small employers that operate without validated backup, encrypting operational files, customer records, and business data and leaving the business unable to recover without paying or rebuilding from nothing
SII builds IT programs for Branford’s organizations that address these risks at costs appropriate to the Connecticut shoreline market.
Why Branford Organizations Choose Managed IT Services

IT for Yale-Adjacent Life Sciences and Technology Companies
Small biotech companies, medical device firms, and technology businesses in Branford’s commercial corridors that operate in the Yale research orbit carry FDA data integrity expectations for regulated data environments, research partnership data governance requirements from academic collaboration agreements, and the vendor security assessments that Yale New Haven Health and other enterprise health system customers send. We build IT programs for Branford’s life sciences and technology community that satisfy these requirements without the overhead that larger enterprise programs carry.

HIPAA for Yale New Haven Health-Affiliated and Independent Practices
Medical and dental practices affiliated with the Yale New Haven Health network carry HIPAA obligations extending to the electronic data flows between the practice and the broader YNHH system. Independent practices serving Branford’s residential community carry the same HIPAA technical safeguard requirements regardless of affiliation. We build HIPAA-compliant IT environments for Branford’s healthcare community at costs appropriate to a shoreline residential community practice.

Seasonal IT for Branford's Shoreline Commercial Economy
Waterfront restaurants, marinas, boat yards, and seasonal commercial businesses in Stony Creek, Indian Neck, Pine Orchard, and Branford’s Long Island Sound communities carry PCI DSS obligations for seasonal-surge payment processing and the operational challenge of IT that must be ready before summer opens and maintained cost-effectively through quieter months. We build seasonal IT programs for Branford’s coastal commercial community that are hardened before the season and reviewed after it closes.

Professional Services IT for Branford's Established Community
Law offices, financial advisors, accountants, and professional services practices serving Branford’s established residential community carry Connecticut professional conduct data security obligations for the accumulated client records of long-standing relationships in a community where professional reputation travels quickly. We build structured managed IT for Branford’s professional services community at costs that fit the shoreline market.

IT for Branford's Commercial and Small Business Community
Retail businesses, restaurants, commercial employers, and small businesses along Branford’s Route 1 and Main Street commercial corridors carry PCI DSS obligations for payment card processing, Connecticut data protection requirements, and the cyber insurance security minimums that commercial property insurers now require. We provide practical managed IT for Branford’s working commercial community.

IT for Light Manufacturers and Commercial Industrial Businesses
Light manufacturers and commercial industrial operations in Branford’s commercial areas carry cyber insurance minimum security controls, Connecticut data protection obligations, and the operational IT requirements of production and commercial businesses that need reliable systems through working shifts. We provide right-sized managed IT for Branford’s industrial and manufacturing community without enterprise overhead.
What Makes SII Different From Other Managed IT Services in Branford, CT?
Our Managed IT Services in Branford, CT
24/7 Infrastructure Monitoring
Continuous monitoring of life sciences and regulated data environments, healthcare EHR and practice management platforms, shoreline seasonal business POS and operations, commercial business applications, and professional services practice management across Branford, with issue detection calibrated to research schedules, clinical hours, seasonal operating windows, and the compliance obligations of each type of organization.
Advanced Cybersecurity Controls
Security built for Branford’s compliance landscape: FDA data integrity-supporting access controls and audit logging for life sciences and technology companies, HIPAA endpoint and network security for YNHH-affiliated and independent healthcare practices, PCI DSS cardholder data controls for shoreline seasonal and commercial businesses, Connecticut professional conduct data protection for law offices and advisory practices, and ransomware and BEC defenses for all Branford organizations.
Cloud Strategy & Management
Research data and regulated environment cloud for Branford’s life sciences companies, EHR and practice management cloud for YNHH-affiliated healthcare practices, POS and hospitality cloud for shoreline seasonal businesses, legal and financial advisory practice management cloud for professional services firms, and Microsoft 365 and productivity cloud for commercial businesses and small employers across Branford’s Route 1 and shoreline corridors.
Network & Connectivity Governance
Reliable network infrastructure for Branford’s life sciences offices, healthcare practice facilities, shoreline commercial businesses from Stony Creek to Indian Neck, and professional services firms along Branford’s Route 1 and Main Street corridors, with the access controls, segmentation, and monitoring that FDA data integrity, HIPAA, PCI DSS, and professional conduct requirements demand.
Business Application Support
Setup and management of regulated research data systems and laboratory information platforms for life sciences companies, EHR and practice management for YNHH-affiliated healthcare practices, POS and reservation systems for shoreline and commercial businesses, and legal and financial advisory platforms for professional services firms serving Branford’s residential community.
Remote Workforce Enablement
Secure device management and access controls for Branford’s life sciences researchers and commercial staff working from laboratory and office locations, healthcare practitioners serving patients across the shoreline communities, professional services employees meeting with clients throughout coastal New Haven County, and seasonal business staff with access needs that change with the calendar.
VoIP & Unified Communications
Business communications for Branford’s life sciences companies coordinating with research partners and commercial customers, healthcare practices running patient scheduling and clinical coordination, shoreline seasonal businesses managing reservations and operations, and the professional services firms and commercial businesses serving Branford’s established shoreline community.
Data Backup & Disaster Recovery
Automated, tested backup for Branford’s compliance-sensitive data: research data and regulated environment records for life sciences companies with FDA data integrity-supporting retention, HIPAA-compliant patient record retention for healthcare practices, PCI DSS transaction record retention for commercial and shoreline businesses, and Connecticut data protection-compliant backup for professional services and commercial organizations.
Ready to Get Started?
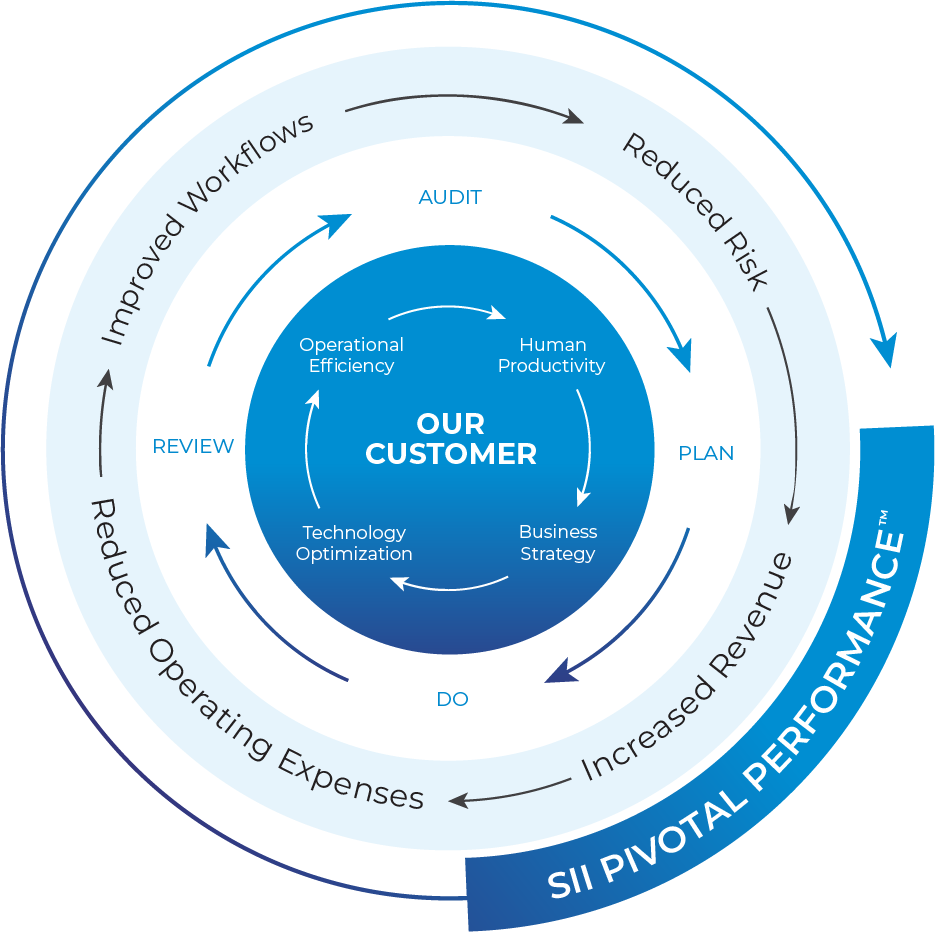
Our Managed IT Operating Model
1
Assess
We review your full IT environment with attention to the compliance dimensions specific to your organization. For life sciences companies, we assess regulated data environments against FDA data integrity requirements and research partnership data governance obligations. For YNHH-affiliated practices, we identify HIPAA technical safeguard gaps including YNHH network data sharing configurations. For shoreline seasonal businesses, we assess PCI DSS cardholder data environment scope and seasonal operational readiness. For professional services firms, we assess Connecticut professional conduct compliance. Every Branford client receives a plain-language written summary before we recommend anything.
2
Strategize
We build a technology plan calibrated to each Branford organization’s planning cycle. Life sciences companies plan around research milestones, FDA submission timelines, and commercial development stages. Healthcare practices plan around patient volume and YNHH network integration. Shoreline seasonal businesses plan around the coastal calendar, with improvements scheduled before summer and reviews after the season closes. Professional services firms plan around client base growth. The plan is cost-transparent and specific to Branford’s shoreline market economics.
3
Stabilize
We close the highest-priority gaps first. For life sciences companies, that means implementing the access controls, audit logging, and data governance documentation that FDA data integrity and research partnership requirements demand. For YNHH-affiliated practices, it means HIPAA technical safeguards and YNHH network data flow controls. For shoreline seasonal businesses, it means PCI DSS cardholder data environment verification completed before the season opens. For professional services firms, it means client data protection and Connecticut professional conduct compliance.
4
Protect & Manage
Ongoing monitoring, security management, help desk support, compliance maintenance, and vendor coordination. For life sciences companies, regulated data environments are monitored with the access logging and integrity verification FDA expects. For YNHH-affiliated practices, HIPAA compliance is maintained continuously across all network data flows. For shoreline seasonal businesses, monitoring is elevated through summer peak and maintained through the quieter months. For all Branford clients, IT problems are handled by our team without requiring the founder, practice manager, or business owner to troubleshoot.
5
Optimize & Review
Regular reviews that give Branford’s life sciences founders, practice managers, firm principals, and business owners the compliance documentation and IT performance reporting they need. Life sciences companies receive FDA data integrity and research data governance documentation. Healthcare practices receive HIPAA compliance status. Shoreline seasonal businesses receive post-season performance reviews and pre-season preparation plans. Professional services firms receive Connecticut professional conduct compliance evidence. We update the technology plan as each Branford organization grows.
Serving Organizations Across Branford and the Connecticut Shoreline
SII provides managed IT services across Branford and the surrounding Connecticut shoreline communities, with structured remote management covering your environment continuously and on-site engineering available throughout Branford and coastal New Haven County. We regularly work with organizations across:
- Branford’s Route 1 commercial corridor, the Branford center area along Main Street, and the commercial and office developments along Leetes Island Road and the surrounding corridors where life sciences companies, technology businesses, healthcare practices, and professional services firms serve Branford’s residential and commercial community
- Stony Creek, Indian Neck, Pine Orchard, Branford Point, and the Long Island Sound shoreline communities where waterfront restaurants, marinas, boat yards, and seasonal commercial businesses serve Branford’s coastal residential neighborhoods and summer visitors
- East Haven, North Branford, Guilford, Madison, and the surrounding Connecticut shoreline communities where Branford-based organizations serve clients and customers, where professional services firms serve the shoreline residential market, and where Branford’s position between New Haven and the eastern shoreline connects organizations to both the Greater New Haven market and the coastal communities stretching toward Old Saybrook
New Haven’s managed IT page covers the Yale research core. Branford is what sits just east of that core: a town that chose its position on the shoreline deliberately, that benefits from Yale proximity without being defined by it, and that has built a commercial and residential community with its own identity and its own IT requirements. We build programs for Branford’s organizations based on that specific character.
Schedule a free IT assessment and find out what a properly structured managed IT program looks like for your Branford organization.
FAQs
We're a small life sciences or medical device company in Branford with research ties to Yale. What IT requirements come with operating in that ecosystem?
Operating as a small company in the Yale research ecosystem creates IT obligations that come from three distinct sources, and understanding which ones apply to your specific situation is the starting point for building the right program. The first source is your research collaboration agreements. If you have data use agreements, material transfer agreements, or sponsored research agreements with Yale or its affiliates, those agreements likely specify how shared research data must be stored, who can access it, and how it must be protected. Depending on the nature of the research, the data may be subject to HIPAA if it involves patient data, to export control regulations if it involves controlled technology, or to institutional biosafety requirements if it involves biological materials. The IT governance of data shared under these agreements must match what the agreements specify. The second source is FDA regulatory requirements. For companies operating in GxP environments, the Electronic Records and Electronic Signatures rule under 21 CFR Part 11 requires that electronic records used to support regulatory submissions have audit trails, access controls, and validation documentation. For medical device companies specifically, the Quality System Regulation under 21 CFR Part 820 applies to the IT systems supporting design controls, CAPA, and complaint handling. The third source is your commercial relationships. If you sell to or partner with hospitals, health systems, or other regulated healthcare entities, their vendor security assessments will ask about your IT security posture. Yale New Haven Health and similar health systems send specific questionnaires to their vendor and research partners, and the ability to respond accurately affects the relationship. We work with Branford’s life sciences and medical device companies to identify which of these three sources apply and build IT programs that satisfy all of them within a single, coherent managed program.
Our practice serves patients in Branford and is affiliated with Yale New Haven Health. What HIPAA IT considerations does that affiliation create?
Yale New Haven Health affiliation connects your practice to one of Connecticut’s most extensive health system networks, and that connection creates HIPAA obligations that extend beyond your practice’s internal systems. The data flows between your Branford practice and other YNHH entities, including referral data, shared patient records, care coordination information, and any data exchanges for quality improvement or population health programs, must use encrypted transmission and be governed by access controls that limit which practice staff can initiate or receive patient data through each channel. Annual HIPAA security risk assessments should document the full scope of YNHH-connected data flows alongside your internal systems, not just the primary EHR integration. For a Branford practice serving a shoreline residential community, many patients also receive specialty or hospital care at other YNHH facilities in New Haven. Those care coordination data flows are worth reviewing specifically to confirm each exchange is appropriately authorized, encrypted, and access-controlled on your end. Business associate agreements should cover the specific data exchanges your affiliation involves. We help Branford’s YNHH-affiliated practices build HIPAA-compliant IT environments that address both the practice-level safeguards and the network integration layer their affiliation requires.
We're a professional services firm in Branford serving established families who have been clients for years. What are our data security obligations?
Connecticut attorneys carry data security obligations under Rule 1.6 of the Connecticut Rules of Professional Conduct, which requires reasonable measures to prevent unauthorized access to or disclosure of information relating to client representation. The Connecticut Statewide Grievance Committee and the Connecticut Bar Association have addressed the application of this rule to digital records, email, and cloud storage, establishing that competent use of technology includes understanding the security implications of the tools used to handle client information. For a Branford law firm serving established families across real estate, estate planning, family law, and general matters, the sensitivity of accumulated client data reflects the depth of those relationships: property records, family financial situations, estate structures, and personal history that clients shared in confidence over years of representation. Financial advisory practices serving Branford’s residential community carry SEC cybersecurity rules for registered advisers alongside Connecticut Division of Securities requirements, and fiduciary data protection obligations that flow from managing accumulated family wealth. The practical IT requirements center on access controls ensuring client files are accessible only to authorized staff, email security protecting attorney-client communications from business email compromise, and tested backup ensuring that irreplaceable client records can be recovered. We build IT programs for Branford’s professional services community that protect the client relationships these practices have built over time.
We run a marina, boat yard, or waterfront business in Stony Creek or along Branford's shoreline. What does our IT program need to look like?
Marine and waterfront businesses on Branford’s shoreline have IT requirements shaped by the intersection of seasonal commercial patterns and the specific operational systems that boat yards, marinas, and waterfront services businesses run. On the compliance side, if you process credit and debit card payments for slip rentals, boat services, fuel, or retail sales, PCI DSS applies to your business and requires network segmentation isolating your payment systems from general business networks, endpoint security on all devices in the payment environment, and annual self-assessment documentation. On the operational side, the systems that matter most are typically your marina management or boat yard management software, your point-of-sale system, and your communications and scheduling tools. These need to be available during operating hours, backed up with tested recovery procedures so that a ransomware attack or hardware failure does not destroy your customer records and booking history, and accessible securely from mobile devices if your staff moves around the property or works remotely in the off-season. On the seasonal planning side, the most valuable thing managed IT does for a shoreline business is move the annual technology review and improvement cycle to the off-season, so that upgrades happen in January and February rather than in the middle of a busy July weekend. We build right-sized IT programs for Branford’s marine and waterfront community that address the PCI DSS compliance, operational reliability, and seasonal planning requirements of shoreline businesses without unnecessary complexity.
Does SII serve Guilford, Madison, East Haven, and the surrounding shoreline communities?
Yes. Many Branford-based organizations serve clients, employ staff, or extend operations to Guilford, Madison, East Haven, North Branford, and the surrounding Connecticut shoreline and inland communities. We manage those environments as a unified IT program with consistent security policies, centralized monitoring, and the same support quality regardless of which shoreline community a location falls in. For life sciences companies with laboratory or office locations in surrounding towns, consistent FDA data integrity controls and research data governance apply at every location where regulated data is accessed. For professional services firms serving clients across coastal New Haven County, remote access security from client offices and home offices along the shoreline is as important as the primary Branford location. For YNHH-affiliated practices with satellite clinical locations, consistent HIPAA-compliant IT governance applies at every site where patient records are accessed. We cover the full Connecticut shoreline footprint each Branford-area client requires.
Branford Chose Its Position on the Connecticut Shoreline Carefully. So Should Its IT.
Get a free IT assessment for your Branford organization. We will evaluate your environment against the FDA data integrity, HIPAA, Connecticut professional conduct, PCI DSS, or research data governance requirements your specific work carries, and build an IT program that fits the character of a town that knows what it wants to be.